PCI DSS Compliant VPS Hosting: What It Means and Why It Matters
What PCI DSS compliance means for VPS hosting and how the shared responsibility model works.
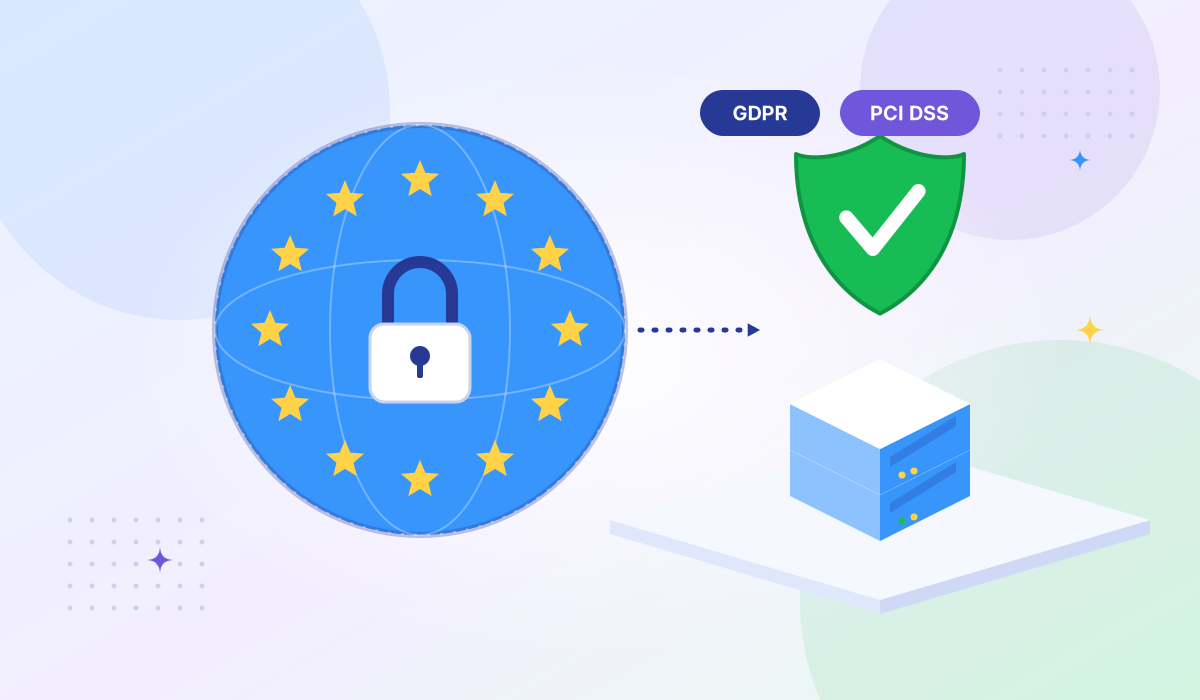
If you serve European customers and process payments, you're dealing with two regulatory frameworks simultaneously: GDPR for personal data protection and PCI DSS for payment card security. They're separate standards with different enforcement mechanisms, but your hosting environment needs to satisfy both.
This guide explains where GDPR and PCI DSS overlap, where they differ, and how to choose hosting infrastructure that meets both requirements without unnecessary complexity.
GDPR (General Data Protection Regulation) protects all personal data of EU/EEA residents — names, emails, IP addresses, browsing behavior, and more. PCI DSS protects specifically cardholder data — card numbers, CVVs, expiration dates, and authentication data.
Despite different scopes, many technical controls overlap:
| Control Area | GDPR Requirement | PCI DSS Requirement |
|---|---|---|
| Encryption in transit | Required ("appropriate technical measures") | TLS 1.2+ explicitly required |
| Encryption at rest | Recommended as a safeguard | AES-256 required for stored cardholder data |
| Access controls | Restrict to authorized personnel only | Unique IDs, MFA, least-privilege access |
| Breach notification | 72 hours to supervisory authority | Varies by card brand (typically immediate) |
| Audit logging | Required for accountability | 12 months retention, 3 months immediately accessible |
| Data minimization | Core principle — collect only what's necessary | Don't store sensitive authentication data post-authorization |
GDPR does not explicitly require that personal data stay within the EU. However, transferring data outside the EU/EEA triggers additional requirements under Chapter V of the regulation:
Hosting in an EU data center (Germany, Netherlands, or similar) eliminates the transfer question entirely. Your data stays in the EU, no additional legal mechanisms are needed, and your compliance documentation is simpler.
Beyond PCI DSS technical controls, GDPR adds requirements that directly affect your hosting environment:
Under GDPR Article 28, you need a signed DPA with any processor handling personal data on your behalf — including your hosting provider. The DPA must specify:
Your infrastructure must support complete data deletion when a data subject requests it. On a VPS with full root access, you control the database and file system, so you can implement deletion procedures. On shared hosting or managed platforms, you may not have this level of control.
You must be able to export a user's data in a structured, machine-readable format. This is an application-level requirement, but your hosting needs to support the database queries and data export tooling to make it possible.
GDPR Article 25 requires that data protection is built into your systems from the start, not bolted on later. Your hosting infrastructure should support encryption, access controls, and logging from day one — not require paid add-ons to enable basic security features.
Here's a practical checklist for setting up a VPS that satisfies both GDPR and PCI DSS v4.0:
Tonic VPS is operated by MB Zaynco LLC, registered in Lithuania (EU member state), providing infrastructure that supports both GDPR and PCI DSS requirements:
No, GDPR doesn't mandate EU hosting. However, hosting in an EU data center is the simplest path to compliance because it avoids the legal complexity of cross-border data transfers. If you host outside the EU, you need adequacy decisions, DPF certification, or Standard Contractual Clauses to cover the transfer — each adding documentation and legal overhead.
The UK adopted its own version (UK GDPR) that mirrors the EU regulation. The European Commission granted the UK an adequacy decision, meaning data flows freely between the EU and UK. For hosting purposes, a UK data center is treated similarly to an EU one for GDPR transfers — though the adequacy decision is reviewed periodically.
GDPR fines can reach up to 4% of annual global turnover or EUR 20 million, whichever is higher. In practice, fines vary widely — from a few thousand euros for small businesses to hundreds of millions for major violations by large companies. The supervisory authority considers factors like the nature of the infringement, whether it was intentional, and what measures were taken to mitigate damage.
Yes, but scope management matters. PCI DSS requires that your cardholder data environment (CDE) is segmented from systems that don't need access to card data. On a VPS, you can achieve this with separate databases, application-level access controls, and network segmentation using iptables rules. If your payment processing scope is small, using a hosted payment gateway (like Stripe's hosted checkout) can significantly reduce your CDE footprint.
Meeting both GDPR and PCI DSS isn't about checking two separate lists — it's about building a hosting environment with strong security fundamentals that satisfy both frameworks. Start with EU-based hosting to simplify data residency, use KVM-isolated VPS for the technical controls, and make sure your DPA is in place.
The controls overlap more than they differ. Strong encryption, proper access management, comprehensive logging, and a documented security policy cover the majority of both frameworks. Where they diverge — GDPR's data subject rights and purpose limitation, PCI DSS's specific cardholder data handling rules — layer those requirements on top of your shared foundation.
Need EU-based VPS hosting for compliance? Explore Tonic VPS plans — EU data centers, KVM isolation, full root access, and reliable uptime backed by enterprise hardware. Operated by an EU-registered company (MB Zaynco LLC, Lithuania).
More VPS hosting guides, server tutorials, and infrastructure tips from our blog.
What PCI DSS compliance means for VPS hosting and how the shared responsibility model works.
Essential security practices every hosting customer should implement from day one.
What uptime SLAs actually guarantee and how to evaluate hosting provider reliability.